VoidSpider: an open-source passive security scanner with a live “spider” graph dashboard
Hi everyone, I’m Patrick, a CS student in Indonesia who also runs a few small game websites and VPS servers. I built VoidSpider, a passive security audit scanner for websites and local files you own.
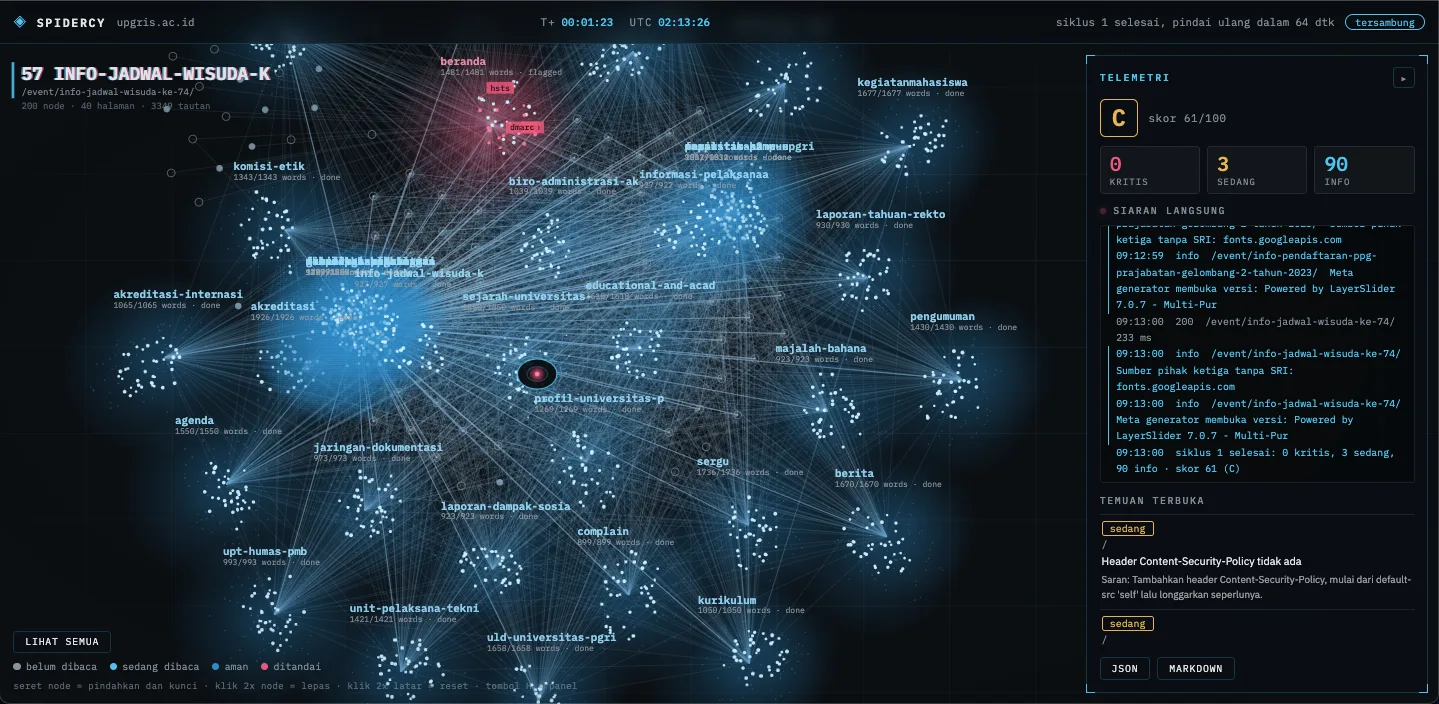
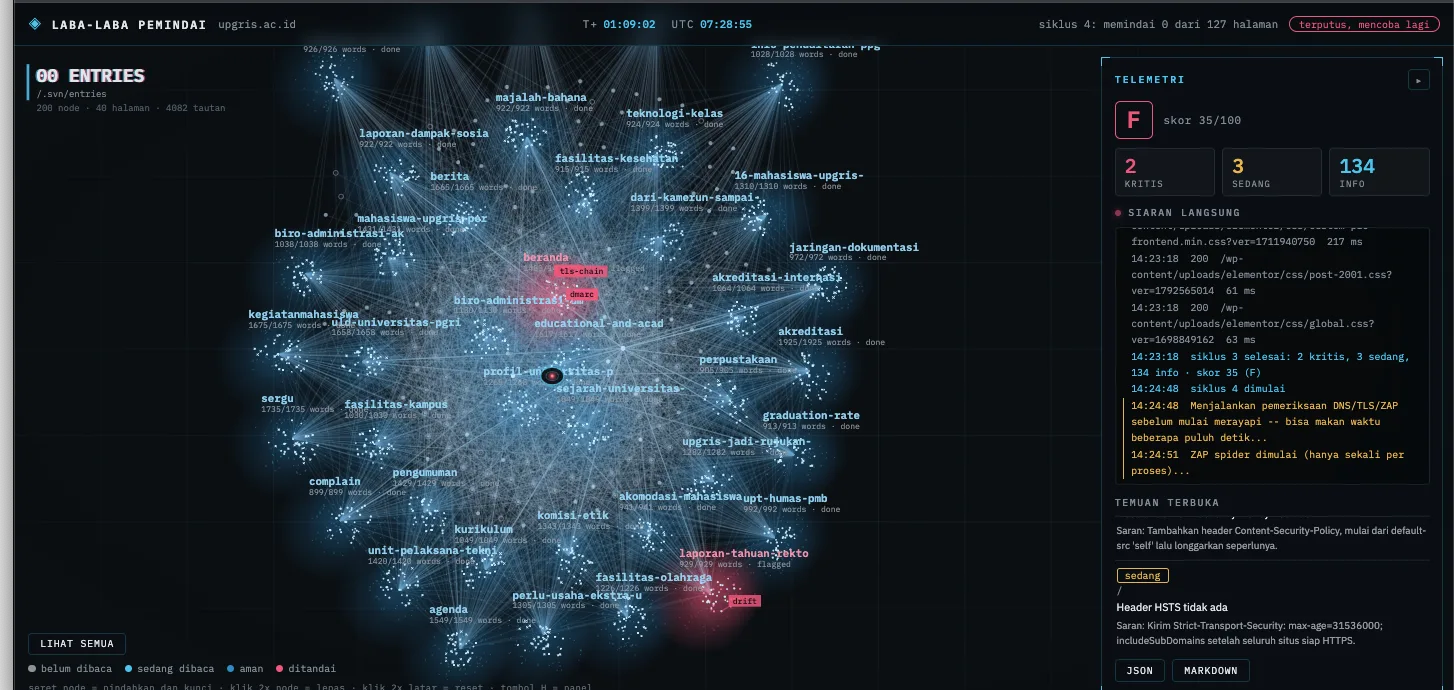
How it works: a Node.js server scans one target continuously and streams results over SSE to a fullscreen dashboard. Each page or file becomes a node cluster, and a geometric spider reaches out to whatever is being scanned right now. Findings get a severity level, a fix suggestion, and an A–F score.
What it checks
Websites: security headers (CSP, HSTS, cookies), exposed files like /.env and /.git/config, leaked keys in HTML/JS, TLS configuration, SPF/DMARC/DNSSEC, and subdomain takeover risk.
Local files: hardcoded secrets, risky code patterns, webshell and obfuscation rules (YARA-style, extendable via JSON), dependency CVEs via OSV.dev, secrets in git history, Dockerfile/Kubernetes/Terraform misconfigs, and invisible-Unicode prompt injection.
Extras: drift detection against a baseline, Telegram alerts, SSH/honeypot log ingestion, SARIF output for CI, and an optional triage agent using Claude that only sees redacted snippets.
A deliberate design choice: it never sends attack payloads, never tries to log in, and never port-scans. Everything is passive GET requests, and it needs an --saya-pemilik-situs (“I own this site”) flag for remote targets. A scanner that can attack works just as well against anyone else’s site. For active testing I added an optional OWASP ZAP integration that you run yourself, with a double confirmation flag.
Honest limitations: it’s pattern-based, so expect false positives and misses. SPAs are only read as far as their initial HTML, and it’s not a replacement for a full SAST or pentest.
Where I’d love feedback:
What passive checks am I missing that you’d want in a first-pass audit? For the entropy-based generic secret detection, how would you reduce false positives further? Is the “passive only” boundary the right call, or too limiting?
Repo (MIT): github.com/patrickivanuellf/VoidSpider