AI agents ran most of a hacker's campaign against 100-plus company websites
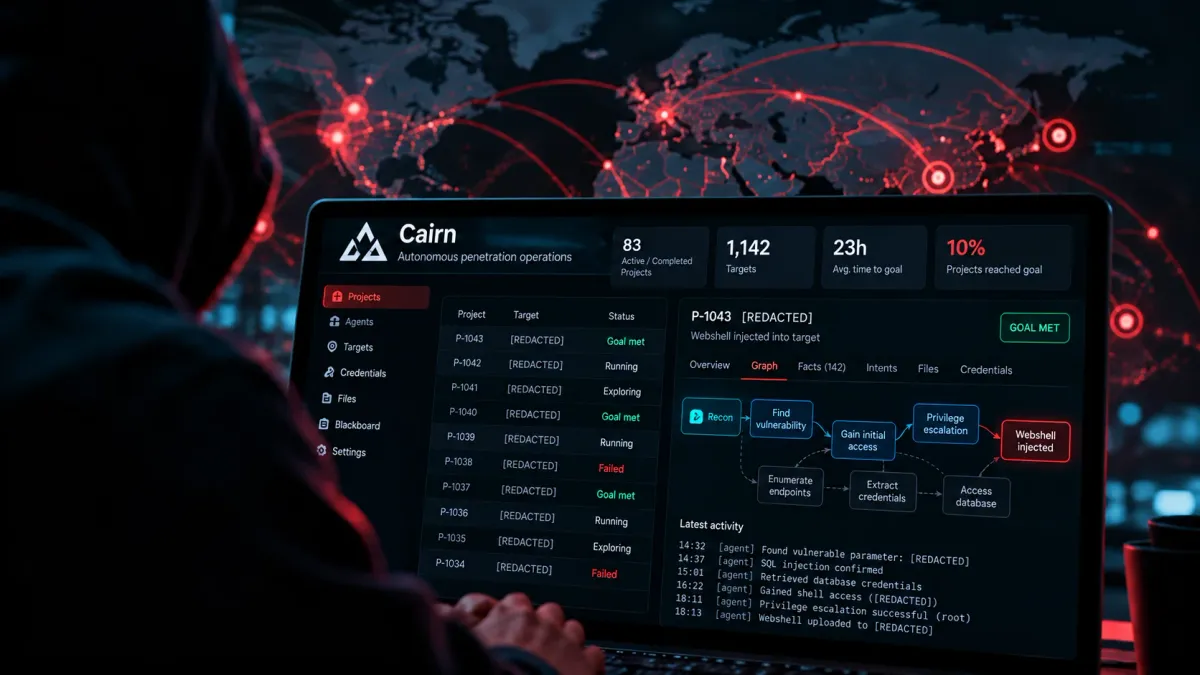
NorForge threat researcher Snorre Fagerland published the findings on Oct. 19. The report traces a Chinese-language operator who used Cairn, an open-source AI penetration testing platform. Cairn's agents do the probing once an operator supplies a target and goal, and the researchers found its control panels publicly reachable. NorForge estimates an average task costs around $5 when failed attempts are included, while noting the figure could be off by a wide margin. The report also found that some apparently legitimate red team operations were exposed through the same panels. Reuters identified some victims by reviewing the hacker's activity. Earlier in September, Gambit Security had reported a criminal campaign using similar AI harnesses. For teams building agent products, an autonomous testing tool left on a public address can become attacker infrastructure. Control panels, credentials and broad tool permissions are the parts to audit before an agent system is exposed to the internet.


