Leak Exposes 41,000 Homeland Security Workers–Including Undercover ICE Agents
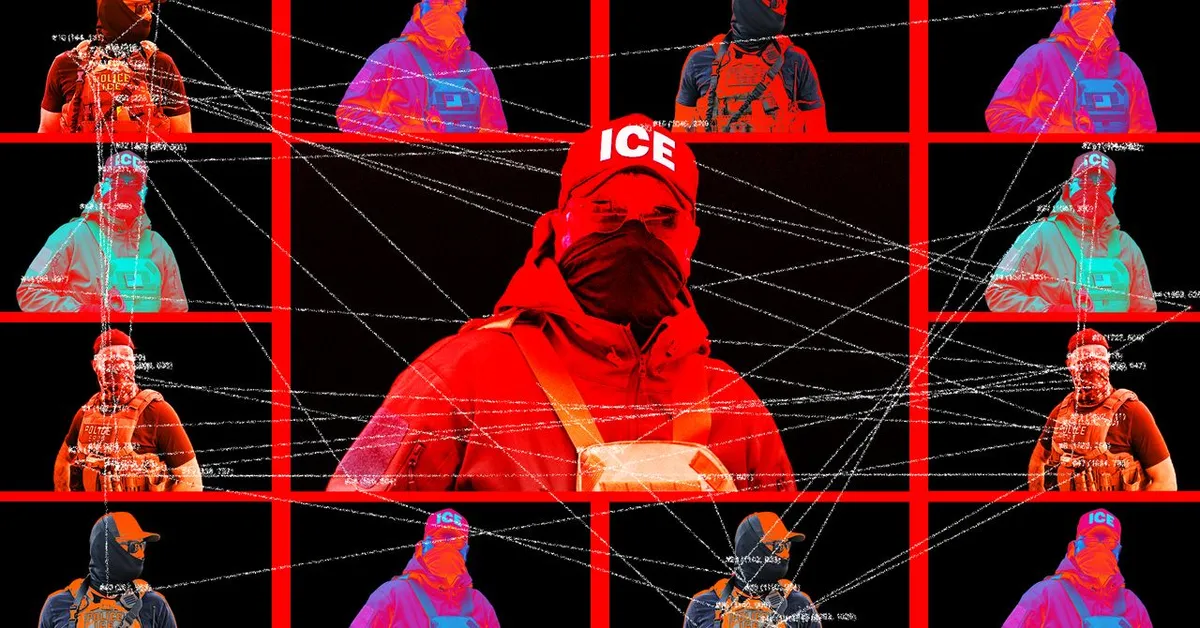
The archive, released October 28 by Distributed Denial of Secrets as Icepick, lists names, email addresses, phone numbers, office locations, job titles, and supervisors. Customs and Border Protection accounts for more than half the records, while roughly 10,000 relate to ICE. The most sensitive layer is over 55,000 permission groups that govern access to internal systems, and WIRED identified 39 Homeland Security Investigations employees in groups containing "CUC," a term government court records link to certified undercover operations. The hacktivist group Department of Peace says it took the records through DHS's Okta single sign-on service, a claim Okta disputes. Reuters matched personal information about six DHS employees named in the leak to credit bureau records and breach data, and confirmed phone numbers by calling three of them directly. One said it was the first they had heard of a breach. Counting a late September claim by the ShinyHunters group over FBI staff data, this is the third major blow to U.S. federal agencies in about a month. For founders, the lesson is that access metadata can reveal as much as the core records. Group names, role tags, and reporting lines let an outsider map who works on sensitive projects. Audit who can read your staff directory and single sign-on group structure, and treat those mappings as sensitive assets.